Audit Agent Router activity
Two complementary Admin Console screens answer the questions a platform operator faces most often: Audit Logs answers who did this? after a configuration changes unexpectedly or a key disappears, and Usage → Analytics answers what is Tetrate Agent Router actually doing? before a quarterly review or a compliance attestation.
Audit Logs is the per-event record. Every administrative action (secret rotation, guardrail change, project membership edit, API key lifecycle event, data-plane change, and similar mutations) is captured with a timestamp, an actor, an actionType, the affected resource, and structured context. Usage Analytics is the aggregated traffic view: organization-wide request counts, token totals, costs, and breakdowns by user, team, API key, and model, with time-range filtering and export. For the full wire schema, see Audit log events.
Persona: Platform operator working in the Admin Console, often under time pressure during an incident or a compliance review.
Estimated time: 10 to 15 minutes for an initial tour; ongoing thereafter.
When this guide applies
| Situation | Surface that helps most |
|---|---|
| Investigating a configuration that has changed unexpectedly | Audit Logs, filtered by resource and time range |
| Identifying who revoked an API key, or when | Audit Logs, filtered by action type |
| Producing a SOC 2, ISO 27001, or other compliance attestation | Audit Logs export, filtered by the relevant time window |
| Forecasting cost across the rest of the quarter | Usage Analytics with a long time range |
| Identifying the heaviest-consuming user or team | Usage → Analytics on the Cost tab, filtered by User or Team |
| Detecting an unexpected spike in spend | Usage Analytics with anomaly inspection, then Audit Logs to correlate to a recent change |
For the developer-side equivalents of the same data (per-request investigation and per-key usage), see Monitor traffic and usage.
Outcomes
By the end of this guide:
- The Audit Logs surface has been opened, exercised, and at least one audit entry has been located with the filters.
- The Usage Analytics surface has been opened and the Cost, API Key, and Model Metrics tabs reviewed.
- A combined investigation pattern ("use Usage Analytics to spot the anomaly, then Audit Logs to find the cause") has been walked through at least once.
- The compliance and retention model is understood, including the immutability guarantee on the log.
Prerequisites
- Administrator access to the Admin Console, typically the
super_adminorbilling_adminrole for Usage Analytics, andsuper_adminfor the full Audit Logs surface. - Some recent activity in Agent Router. A freshly installed Agent Router with no traffic and no administrative changes surfaces empty screens that are technically working but uninformative.
Step 1: open audit logs and orient
-
Sign in to the Admin Console.
-
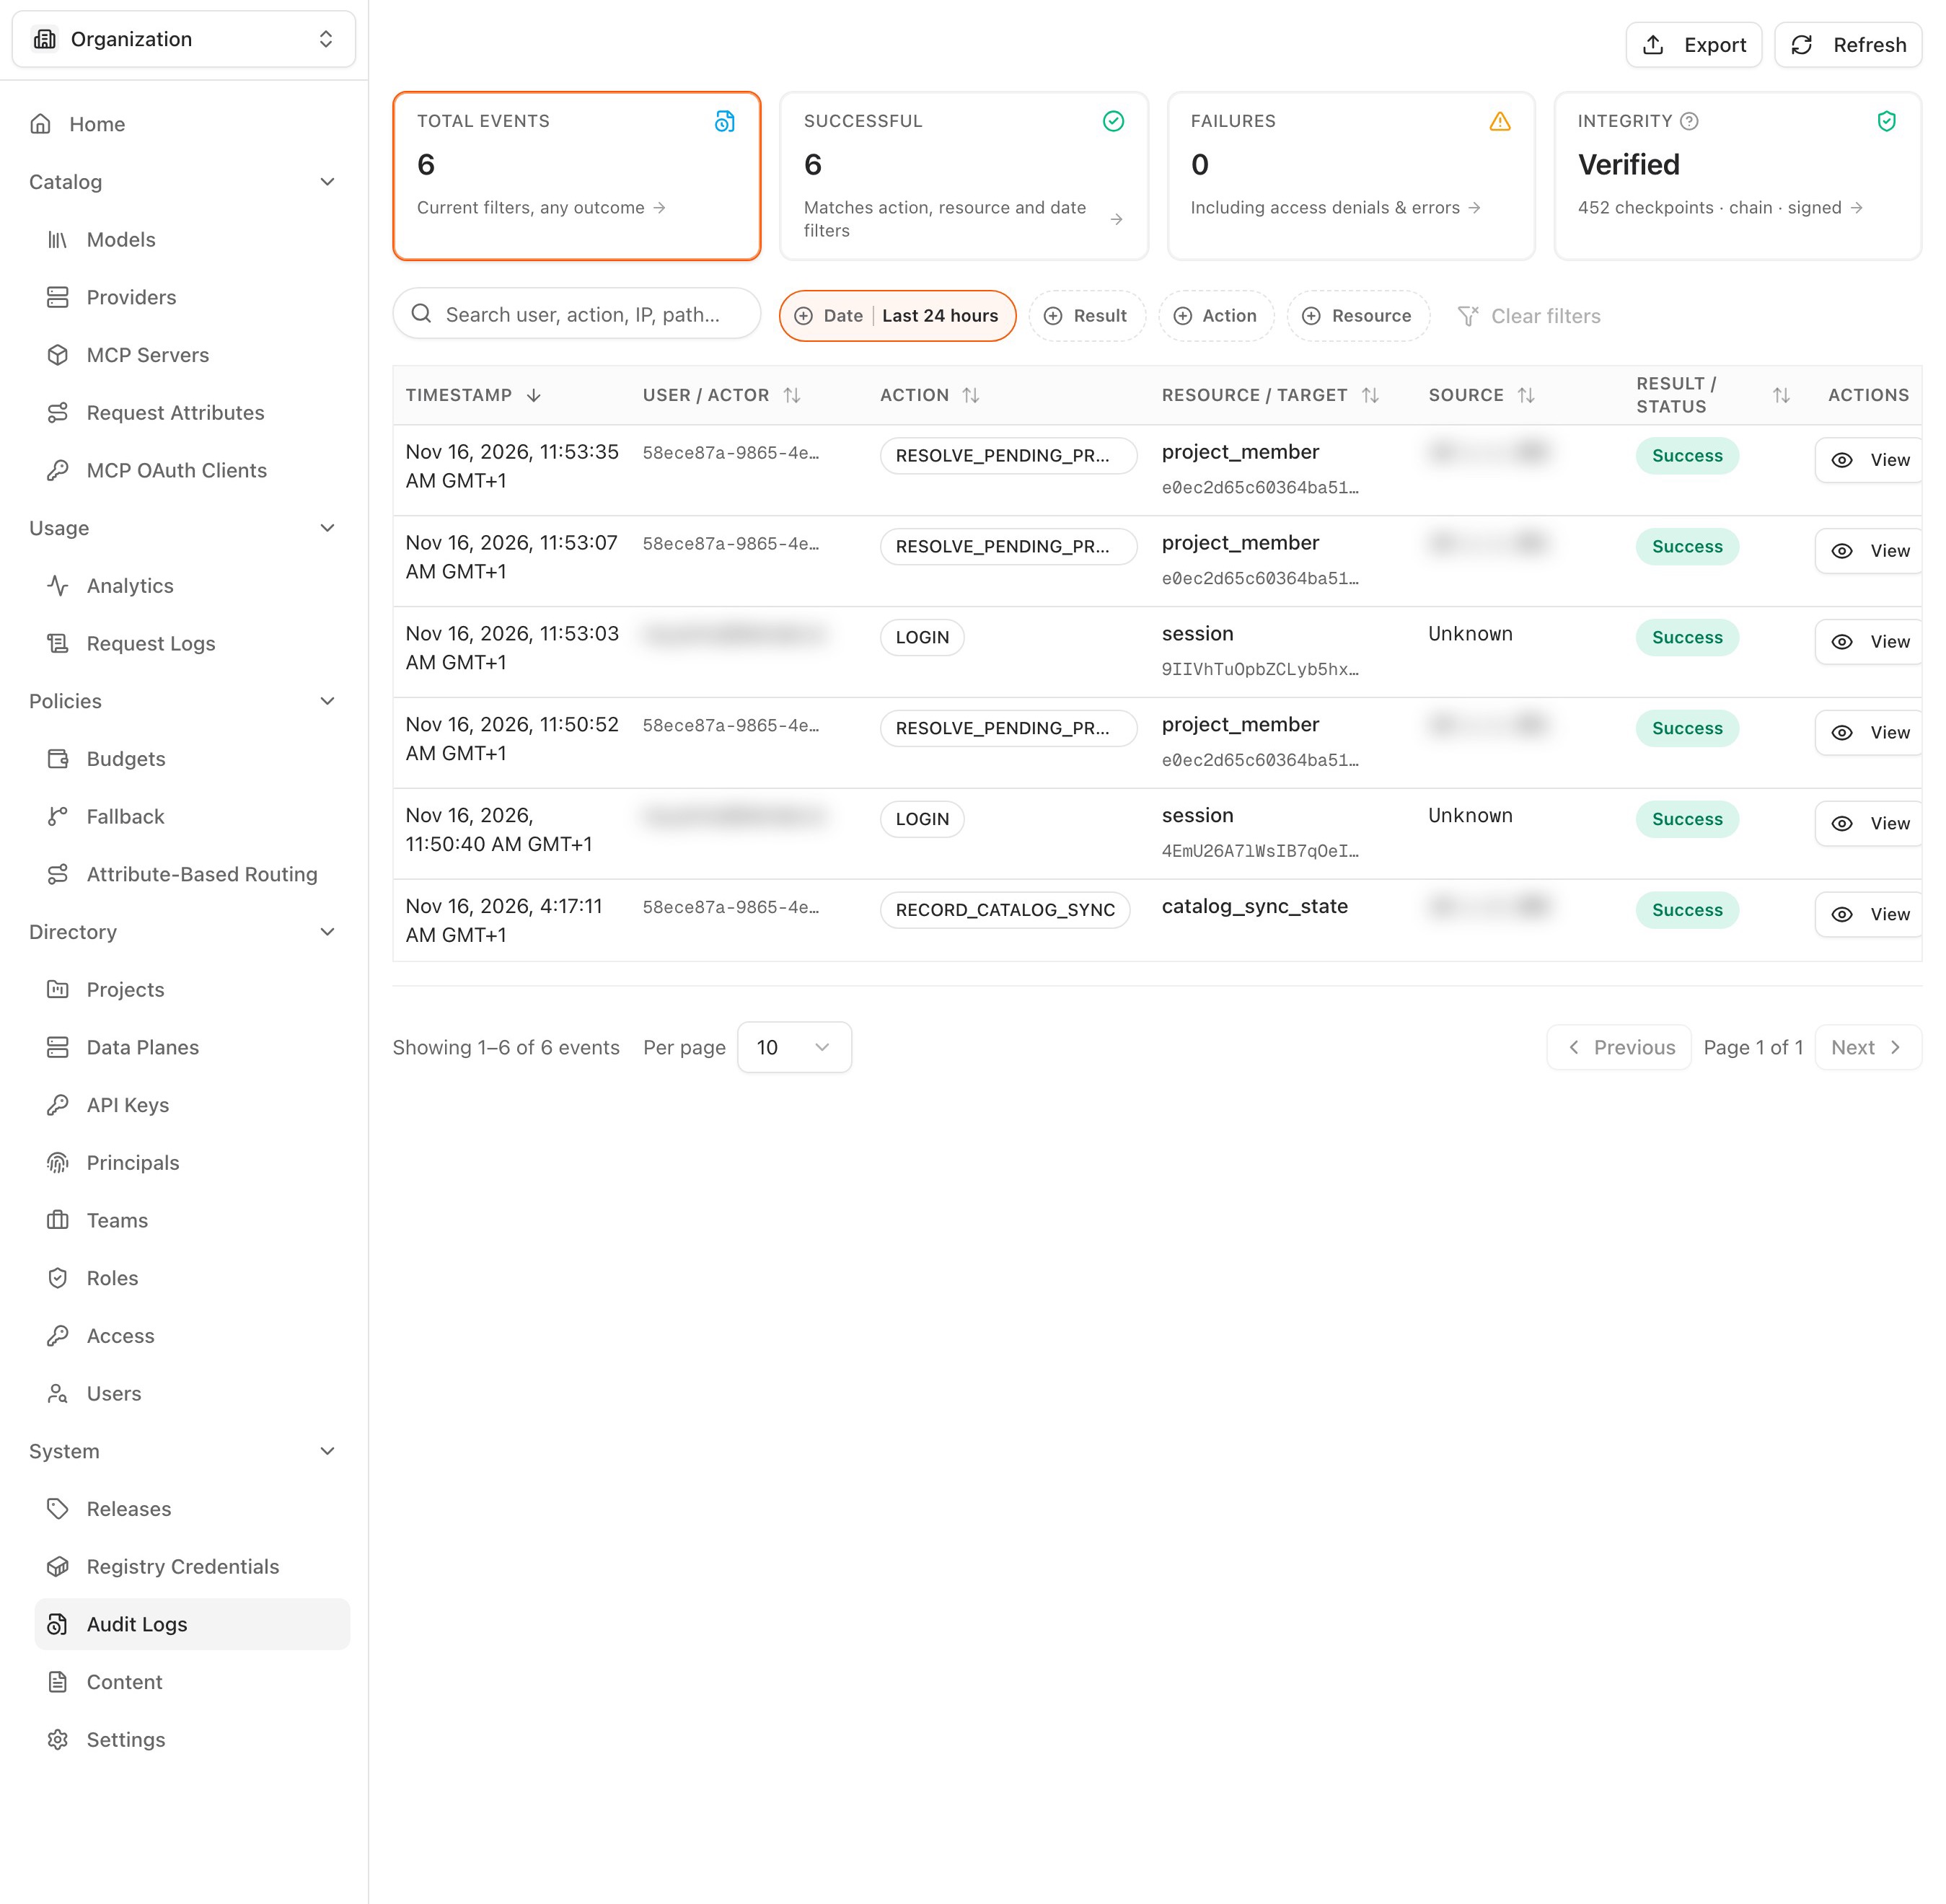
Open Audit Logs from the sidebar. From 0.12.0, the page opens on the last 24 hours, and older events are one click away in the Date filter (a longer preset or All time).
-
Review the columns surfaced for each entry:
Field What it carries Timestamp Date and time in the browser's time zone, with the zone named (for example Nov 10, 2026, 2:15:03 PM EST). The format follows the browser's language. The details panel shows the same valueUser / Actor The acting user id (and email when available). An event whose user has no email shows the user's name from the user directory, with the ID underneath and a copy button. An event with no user, such as one written by a service, reads Service. From 0.9.0, a change made through a console names the signed-in person, and the console's key ID moves to metadata.via_keyAction Wire actionTypesuch asCREATE_SECRET,SET_GUARDRAIL_STATUS, orDELETEResource resourceTypeplusresourceId, often with a human-readable label in the UISource Origin of the request when known Result Success or failure, with HTTP status when available. Events that were not web requests, such as logins and background jobs, show no status. From 0.9.0, a refused or failed change leaves one failure entry -
Entries appear in reverse chronological order, with the most recent action at the top of the list.
Action names are stable uppercase strings on the wire (CREATE_SECRET, UPDATE_GUARDRAIL, ADD_PROJECT_MODEL), not dotted <resource>.<verb> labels. Common examples:
| Action type | Generated when |
|---|---|
CREATE_SECRET / DELETE_SECRET / ROTATE_SECRET | Secret lifecycle |
SET_GUARDRAIL_STATUS / CREATE_GUARDRAIL / UPDATE_GUARDRAIL | Guardrail enablement and edits |
ADD_PROJECT_MODEL / REMOVE_PROJECT_MODEL | Project model catalog changes |
ADD_PROJECT_PROVIDER / REMOVE_PROJECT_PROVIDER | Project provider attachment |
CREATE_CLIENT_KEY / DISABLE_CLIENT_KEY / DESTROY_CLIENT_KEY | API key lifecycle |
ISSUE_MY_KEY / REVOKE_MY_KEY | A management key issued or revoked by its owner. From 0.9.0, these replace the Developer Console's own record |
ADD_PROJECT_MEMBER / UPDATE_PROJECT_MEMBER / REMOVE_PROJECT_MEMBER | Project membership |
AUTO_JOIN_DEFAULT_PROJECT | A user joined the organization's default project automatically. The management API has written it since 0.11.0, and from 0.12.0 it also replaces the Admin Console's project_member.auto_join, and the joining user is the entry's subject, not its actor |
BAN_USER / UNBAN_USER / ADD_USER_GROUP_MEMBERS / REMOVE_USER_GROUP_MEMBERS | Ban, unban, and team changes on the Users page. From 0.12.0 these are the only records for those changes. A bulk ban that leaves some users unbanned is recorded as a failure |
UPDATE_PRINCIPAL_CALLER_KIND | An admin corrected whether a principal is a person or an application, with the old and the new kind. Recorded from 0.12.0 |
CREATE_DATAPLANE / UPDATE_DATAPLANE / DELETE_DATAPLANE | Data plane lifecycle |
FINISH_DATAPLANE_UPGRADE | A data plane upgrade ended; the final phase is in metadata.phase, and only Completed counts as a success. Recorded from 0.9.0 |
PROJECT_SERVED_NOWHERE | A project lost the last data plane serving it: its last label was removed, it was detached from its last data plane, or a data plane delete left it unserved. Recorded from 0.7.0 |
CREATE_TELEMETRY_CONFIG / UPDATE_TELEMETRY_CONFIG | Telemetry and SIEM forward configuration. From 0.9.0, these also replace the Developer Console's telemetry.project_config.set and telemetry.project_config.disable entries |
AUTHORIZATION_DENIED | A management API call refused for missing permissions on the identity, tenancy, API key, AI key, model catalog, MCP, RBAC, and Developer Console request-log APIs, with the operation in the resource column. Recorded from 0.9.0; refusals on other endpoints are not recorded yet |
See Audit log events for the full field list and a broader vocabulary sample. The record names that changed in 0.12.0 are in Changes in 0.12.0.
From 0.13.0, a failed SSO, SAML, social, or command line sign-in writes a failed LOGIN record, so failed sign-ins appear under Audit Logs alongside successful ones. Past a rate limit, further failures are counted in one summary record instead of one record each, so a burst of failures shows as a count, not as a long list of rows. New sign-in sessions record the user agent, and user agents and error messages on these records are cut at 512 bytes and marked as cut. Changes to telemetry export settings name the signed-in user. The client address on these records depends on a management plane setting that Tetrate runs, so no customer step is needed. See Changes in 0.13.0.
From 0.11.0 the management API writes the only record when a project's providers or models are added or removed, a project is edited, a project's MCP servers are added or removed, a catalog sync starts, a project's preferred endpoint is starred, or SSO settings are saved. Until a later release removes the Admin Console's remaining audit writes, any other Admin Console change that the management API also audits appears twice, and both entries name the signed-in user: for example, UPDATE from the console and UPDATE_DATAPLANE from the management API. The management API's entry is the one that carries metadata.via_key. The other changes in 0.9.0 that affect SIEM rules are listed under Changes in 0.9.0.
Step 2: investigate a specific change
An Audit Logs investigation is a sequence of filters, which can be combined: the more specific the combination, the smaller and more useful the result set. The filters are Date, Result, Action, and Resource, and the search box covers the rest.
- Set the Date filter to the window around the moment of interest. A narrower window is almost always more useful than a wider one. The filter offers Last 24 hours, Last 7 days, Last 30 days, Last 6 months, All time, or a custom range picked on the calendar. The filter always shows the range in use. A custom range uses the viewer's own days: a picked day runs from midnight to midnight in the browser's time zone. Clicking ✕ on the filter, or clearing the calendar, returns to the last 24 hours.
- To find one person's actions, type their email or user ID in the search box. The page has no Actor filter. The search box matches the user's email and ID, the actor type, the action, the resource type and ID, the correlation ID, the endpoint, the source IP, and the error message. A search with no start date covers the 30 days before the end date (or today), and the page says so under the search box. All time sends no start date, so the 30 days apply there too.
- Apply the Action filter if the type of change is known, for example
REMOVE_PROJECT_PROVIDERif a provider detachment is suspected. - Apply the Resource filter to narrow the entries to one resource type. To find one resource, type its ID in the search box: a model id, a provider id, a secret name, or an API key's ID (the
idthe API returns). Neither console shows the key's ID, and a key's UID does not match an audit record. - Open View on the resulting entries.
metadata, request context, and result fields usually identify what changed.
Paging keeps the list still: moving between pages reads the same fixed window of time, so rows and the total do not shift and no row repeats or is skipped. Refresh, changing a filter, or picking a range moves the window up to now and returns to page 1, and events that arrived since appear then. When a preset range comes back empty, the table says so (for example, "No matching audit events in the last 24 hours.") and suggests a longer range from the Date filter.
A worked example: a developer reports that requests targeting gpt-4o started failing yesterday afternoon. To investigate:
- Set the Date filter to a custom range covering yesterday afternoon, plus a couple of hours of buffer on either side.
- Filter on the model or provider resource associated with
gpt-4o. - Review the resulting entries. A
REMOVE_PROJECT_MODELorREMOVE_PROJECT_PROVIDERaction in that window would explain the symptom immediately. - If no model-level change shows up, broaden the search by removing the resource filter and looking for related
actionTypevalues on the same provider in the same window.
Step 3: open usage analytics and orient
Usage Analytics shares the same time-range model as Audit Logs, and the two are designed to be used together.
-
In the Admin Console, open Usage → Analytics from the sidebar.
-
Review the top-level metrics on the Cost tab: Spend (counts toward budgets), Estimated, Total Requests, and Total Tokens.
-
Apply a time range at the top of the page. Presets cover last 24 hours, last 7 days, and last 30 days; a custom range covers anything longer or more specific.
-
Switch between the available tabs:
Tab What it lists Cost Requests, tokens, and cost by API key, user, caller, sign-in method, and team Tokens Input, cache read, cache creation, and output tokens by the same dimensions API Key Each API key with its user, caller, sign-in method, requests, input and output tokens, total cost, and last use Errors Errors by model, split into 4xx and 5xx responses, with average latency and top status codes Clients Tools reported by callers, with requests, errors, success rate, tokens, and cost Model Metrics Requests and Avg, P50, P90, P99, Min, and Max values by model MCP Tool requests, errors, average latency, and share of total, grouped by tool
The User and Team filters limit the Analytics view to selected users or teams. To select several users or teams at once and compare them side by side, see Compare user and team spend in Analytics.
This surface differs from the developer-side Usage page in the Console:
| Feature | Admin Usage Analytics | Console Usage |
|---|---|---|
| Scope | All users and API keys | The signed-in user's own data |
| Breakdowns | User, team, API key, model | Model, API key |
| Cost analysis | Organization-wide cost totals and per-user costs | Individual user costs |
| Export | Full Agent Router data export | None |
| Audience | Agent Router administrators | Individual developers |
Step 4: combine the two surfaces in an investigation
Most investigations cross both surfaces. The most reliable pattern:
- Spot the anomaly in Usage → Analytics. An unexpected cost spike on the Cost vs. Token Over Time chart, an unfamiliar model on the Model Metrics tab, an outlier in the Cost tab table.
- Identify the resource. Filter Analytics down to the specific user or team the anomaly points at.
- Switch to Audit Logs. Apply the same time window plus the resource filter.
- Look for an administrative event. Most surprising traffic patterns are explained by a recent configuration change: a new model enabled, a routing change, a user role modified, or an API key reissued.
- Reconstruct the timeline. The combination of the audit entry and the usage chart shows what changed, who changed it, and the resulting traffic shift.
The reverse direction (starting from an audit event and looking for its traffic consequences) is equally common. A recent ADD_PROJECT_MODEL event makes a model appear on the Model Metrics tab; these correlations are how the "did the change have the intended effect" question is answered.
Step 5: export for compliance and reporting
Usage Analytics supports export of the filtered data:
- Apply the time range and filters that match the report being produced.
- Click Download CSV.
- The downloaded file contains the metrics for the selected filters and time range.
Audit Logs export, where supported by the deployment, follows the same shape. The exported records are the same immutable rows that the screen displays, with all of the audit fields included.
A pipeline that pulls one organization's records through the management API uses QueryCustomerAuditLogs and GetCustomerAuditLog from 0.10.0. These return the organization's project, project member, AI key, model assignment, MCP profile, MCP OAuth client, API key, budget alert, data plane, and project gateway changes, among others; records written before the 0.10.0 upgrade carry no organization and are not returned. QueryAuditLogs is the fleet-wide read and needs a platform grant; an organization admin calling it is deprecated. The grants and record types are in Audit log events.
Compliance posture
The audit surface is built to satisfy the audit and integrity requirements of SOC 2, ISO 27001, and similar frameworks, through three properties:
- Immutability. Audit entries cannot be edited or deleted by any user, regardless of role. There is no "delete from the log" operation anywhere in the Admin Console.
- Coverage. Every state-modifying administrative action generates an entry. There is no path through the Admin Console that changes Agent Router state without leaving a record. From 0.9.0, the entry is written in the same transaction as the change, and an entry that cannot be written is counted in the management plane's
audit_write_failures_totalmetric, which is worth an alert. - Retention. The retention period for audit data is set by the deployment configuration. Long-horizon retention, including compliance-archival use cases, is supported through export to an external system; the Admin Console window is intended for active investigation rather than indefinite storage.
Where to go next
Configure SSO
The SSO surface generates audit events this guide makes visible.
Working with budgets
Budgets track spend, raise alerts, and can enforce a spend ceiling, and are visible in Usage Analytics.
Run multiple Agent Router instances
Multi-instance deployments need to be audited per instance; the audit surface helps confirm that boundary.