Self-hosted onboarding
Onboard a Self-Hosted Data Plane deployment through a one-time Admin Console wizard. Steps 1 to 5 collect configuration, Step 5 downloads the credential used to install the data plane, and Step 6 confirms completion.
The onboarding wizard
The wizard launches automatically on the first sign-in to the Admin Console; there is no separate onboarding URL. Each step has Next and Previous controls. Next is enabled once the current step's required fields are filled; Previous returns to any earlier step to review or change a value.
Step 1
Organization Name
Identify the tenant.
Step 2
Corporate Login
Configure SSO over OpenID Connect (OIDC). Sign-in after onboarding depends on it.
Step 3
LLM Providers
Connect providers such as OpenAI and Anthropic.
Step 4
LLM Models
Choose which models are exposed.
Step 5
Configure data plane
Download the data plane credential file (data-plane-credentials-default.json) the data plane needs.
Step 6
Setup Complete
The Admin Console can now be accessed by signing in with SSO.
Onboarding produces a configured management plane and a data plane credential file (data-plane-credentials-default.json) used as input to the data plane installation. Plan for 15 to 30 minutes, plus any back-and-forth with the identity provider (IdP) team.
Prerequisites
The environment checklist (browser, network, cluster, and SSO details) is on the Prerequisites page and is assumed complete here. The wizard itself needs four things on hand:
- Access to the Admin Console, using the sign-in details Tetrate provides during provisioning. The wizard launches on that first sign-in.
- API credentials for at least one LLM provider, for example an OpenAI API key.
- OIDC IdP details (issuer URL, client ID, client secret, scopes), and an IdP administrator reachable during Step 2 to register the redirect URI the wizard displays. Agent Router supports OIDC only. See SSO configuration.
- Optionally, the hostnames client applications will call, for example
ar-proxy.my-company.com. They are not entered in the wizard. They are declared in the data plane's chart at install time, as described in Declare the hostnames a data plane serves.
Get started
Click Start setup to begin.
Step 1: configure organization name
Fill in:
| Field | Required | Description | Sample value |
|---|---|---|---|
| Organization Name | Yes | The organization's display name | Acme Corp. |
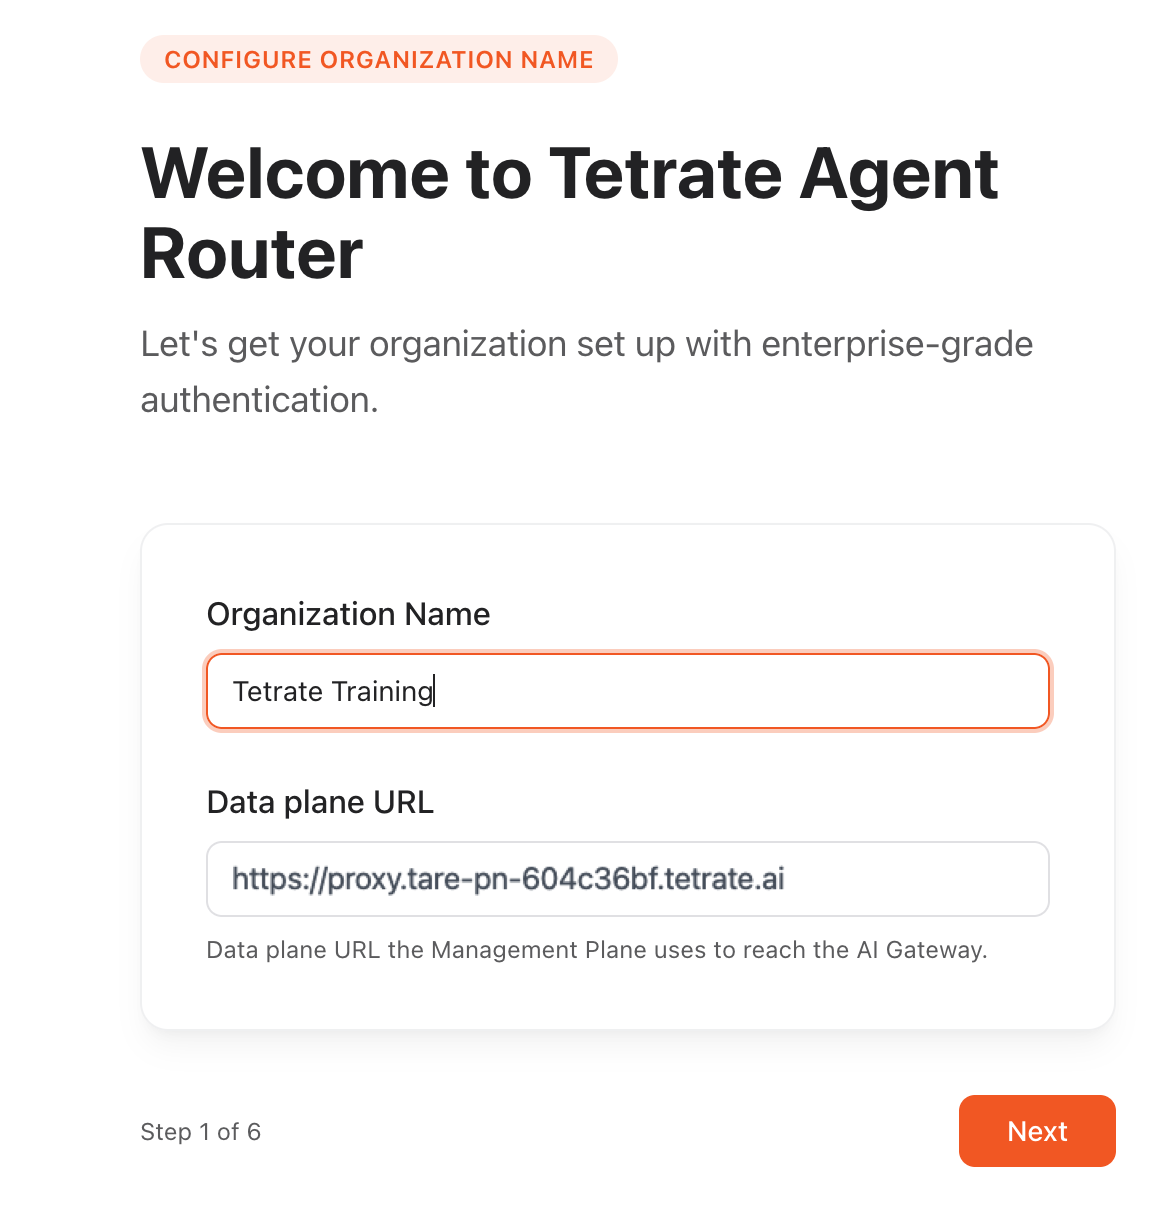
Since 0.7.0 the wizard does not ask for a data plane URL. The data plane declares the hostnames it serves in its own chart (global.gateway.hostnames, or tare install --gateway-hostname), and reports them to the management plane once it is installed. Until the data plane reports, the completion screen shows Your default project isn't serving traffic yet. The notice clears on the data plane's first report, either with the hostnames its chart declares or with its first status report. See Declare the hostnames a data plane serves.
Before 0.7.0 the wizard carried an optional Data plane URL field that stored one gateway address for the data plane. An address stored that way keeps working for a data plane whose chart declares no hostname.
Step 2: configure corporate login (single sign-on)
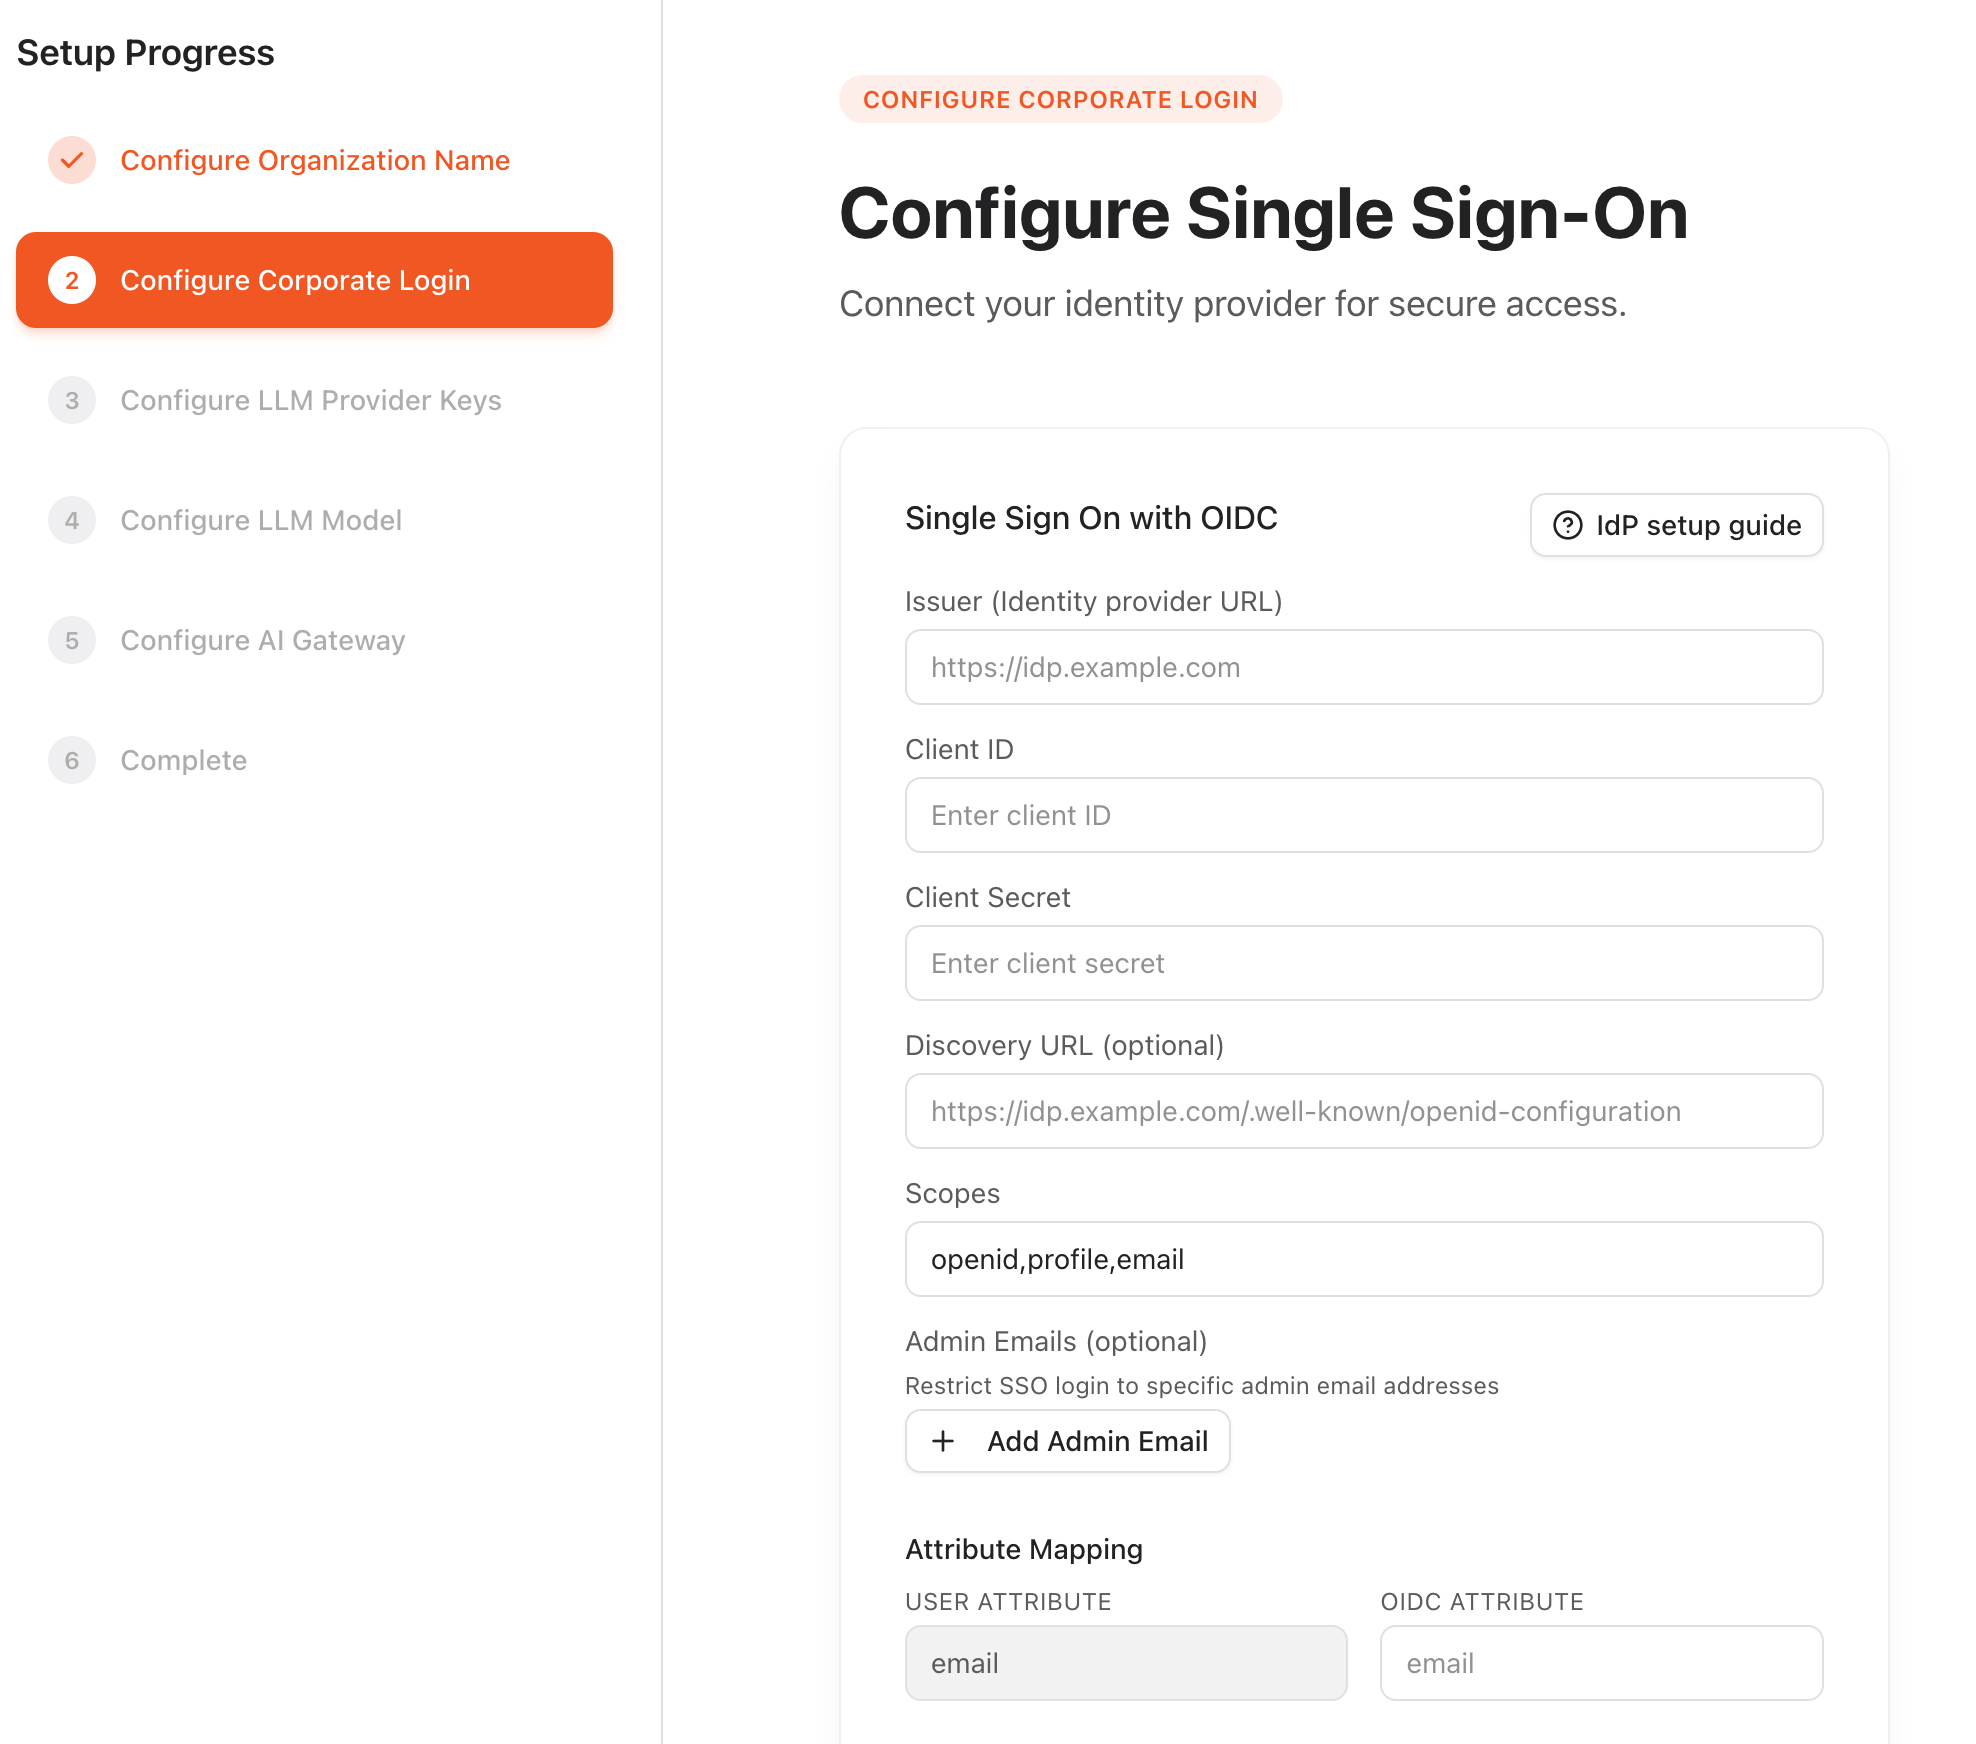
Configure SSO in this step. No local account is issued alongside it, so the Console and the Admin Console are reached through the identity provider once the wizard finishes, and skipping the step leaves no way to sign back in. Details of the IdP side are in the SSO configuration guide.
Agent Router supports OIDC only. SAML, LDAP, and other protocols are not supported.
The wizard displays the OIDC redirect URI for the deployment, following the pattern:
https://dashboard.<your-mp-host>/login
Register Agent Router as an OIDC application in the IdP using that exact URI, then fill in:
| Field | Required | Description | Sample value |
|---|---|---|---|
| Issuer (IdP URL) | Yes | OIDC issuer URL exposed by the IdP | https://login.example.com/ |
| Client ID | Yes | OAuth client ID created for Agent Router | agent-router |
| Client Secret | Yes | OAuth client secret paired with the Client ID | •••••••• |
| Discovery URL | No | OIDC discovery document URL. If omitted, Agent Router constructs it as <Issuer URL>/.well-known/openid-configuration. | https://login.example.com/.well-known/openid-configuration |
| Scopes | Yes | OAuth scopes to request | openid profile email |
| Admin email | Yes | At least one user granted admin rights after the first SSO login | [email protected] |
| Attribute mapping | Yes | Maps an IdP claim to the Agent Router user's email. The typical value is email. | email |
Step 3: configure LLM provider(s)
Connect Agent Router to one or more LLM providers. At least one provider is required to route traffic.
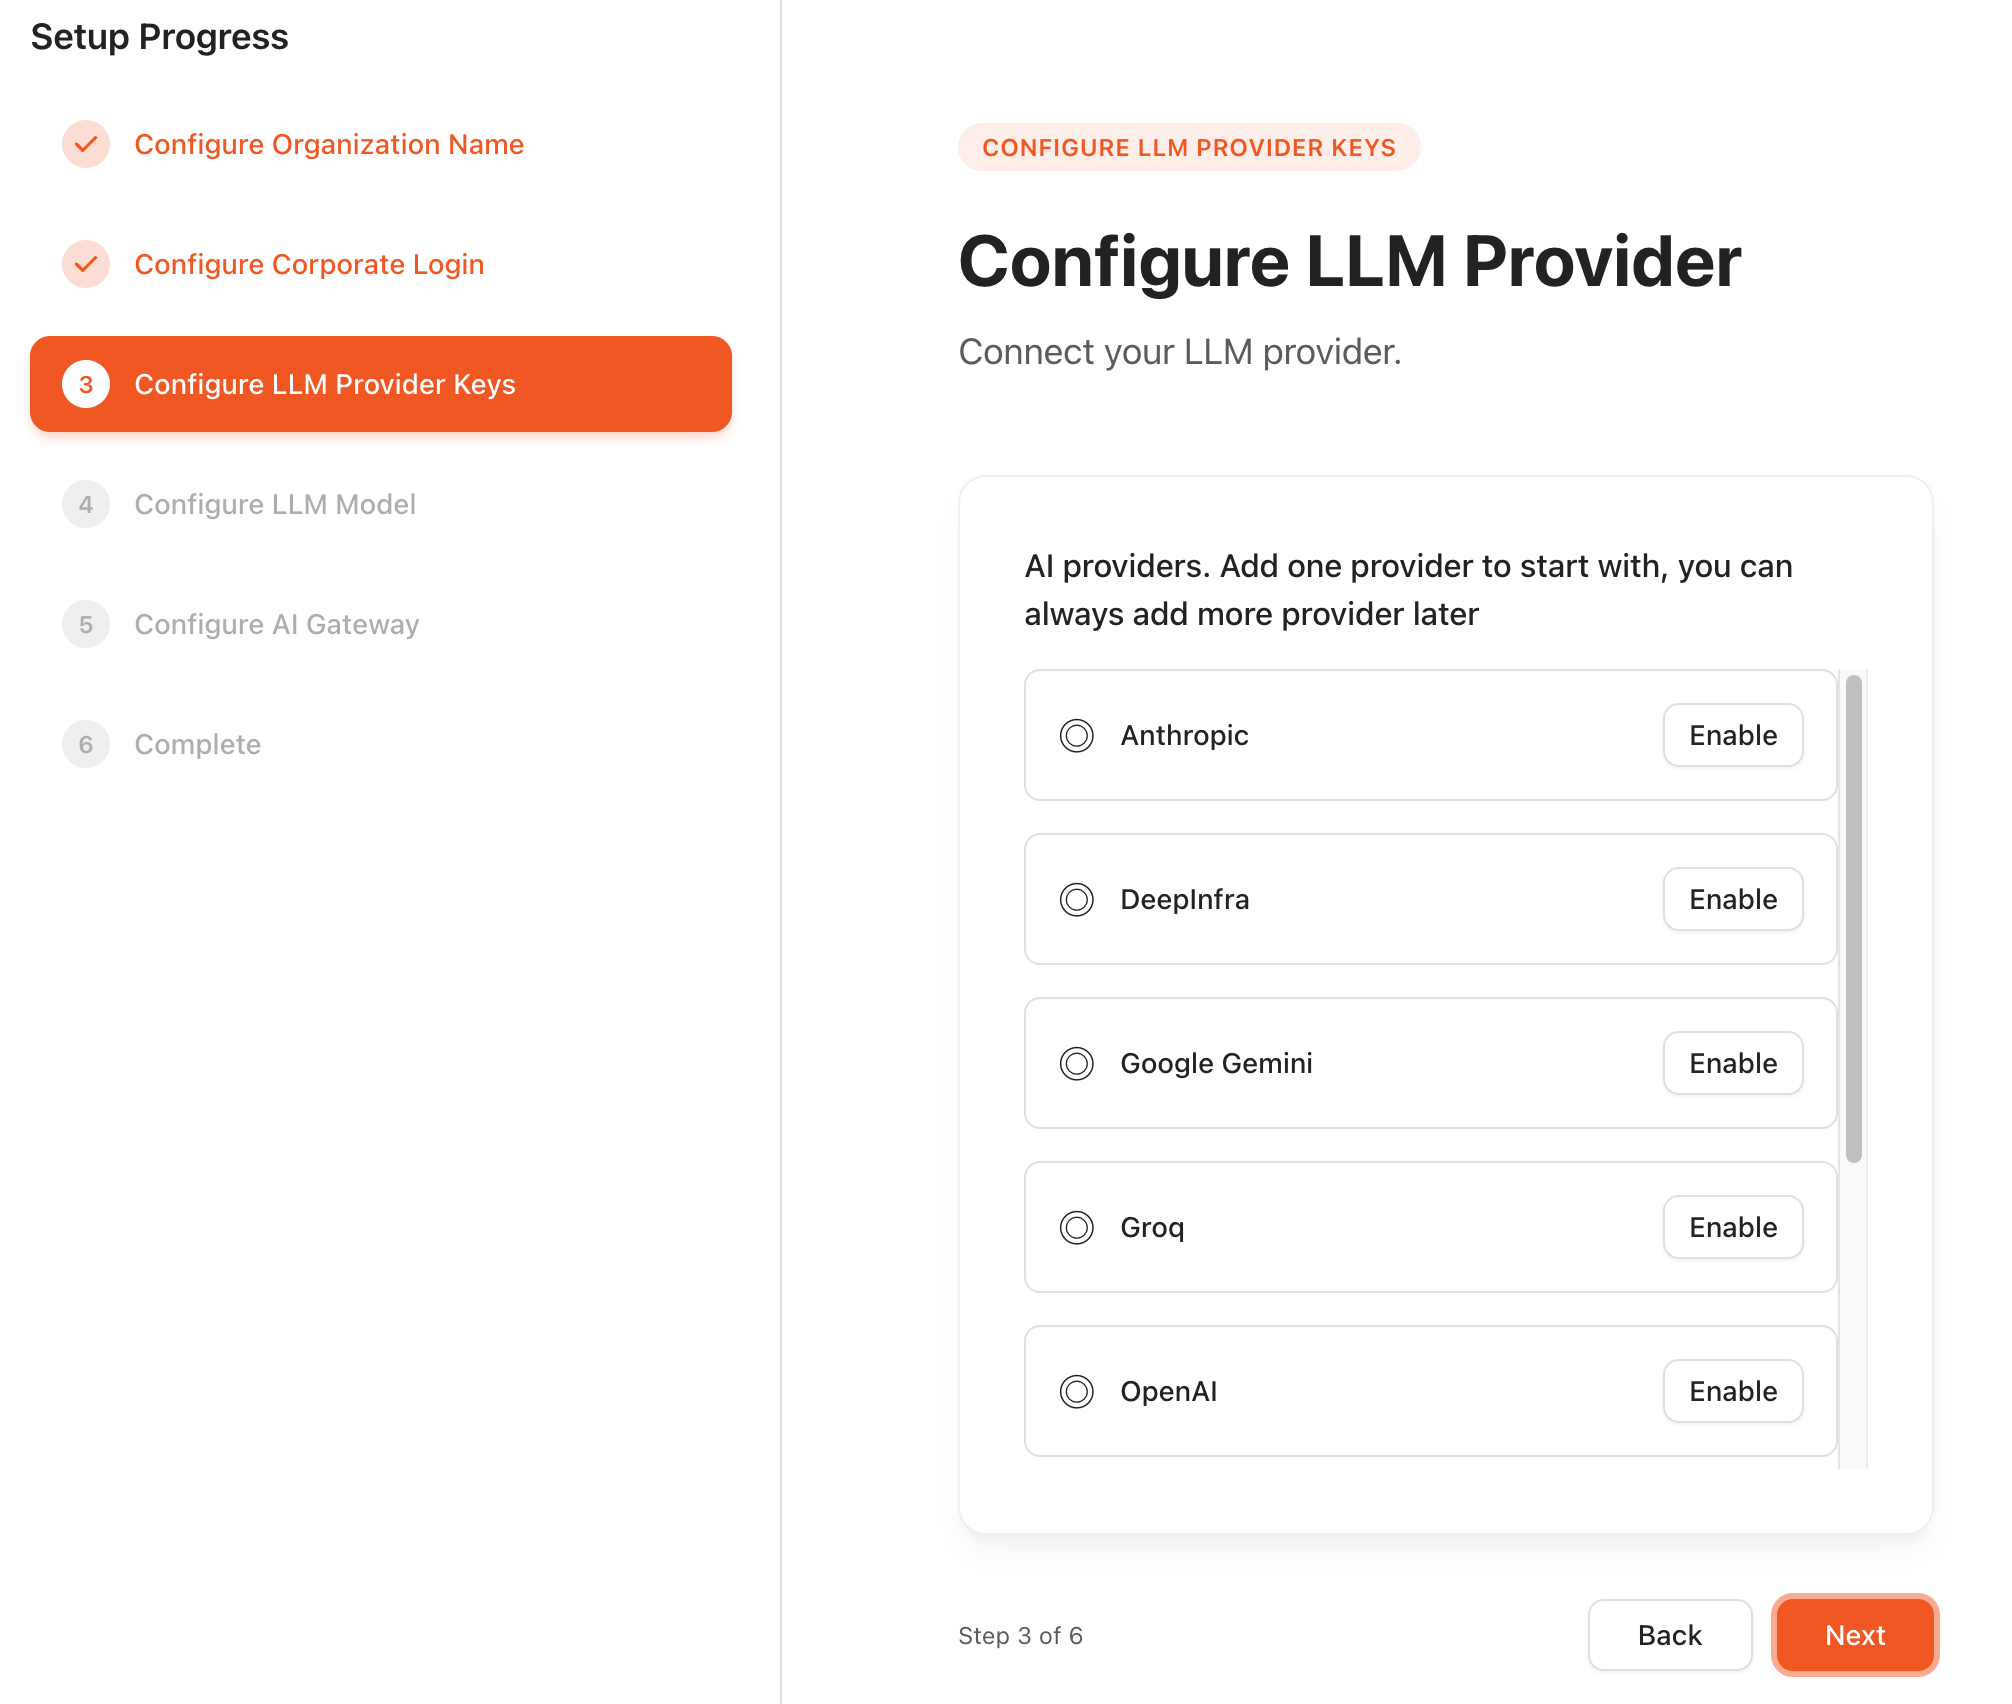
The wizard shows a radio button for each supported provider, including OpenAI, Anthropic, Google, Azure OpenAI, Mistral, Cohere, Together, and Perplexity. See Provisioning models and providers for the authoritative list. Select a provider, click Configure, then fill in:
| Field | Required | Description | Sample value |
|---|---|---|---|
| Display Name | No | Optional label shown in tables and filters | OpenAI |
| API Base URL | Yes | Base URL for the provider API. Pre-filled for supported providers. | https://api.openai.com/v1 |
| Auth method | Yes | Authentication method. Pre-filled per provider. | API Key |
| Secret Type | Yes | Password for single-string API keys; Service Account JSON for providers that authenticate with a JSON credential file. | Password |
| Provider Secret | Yes | API key, token, or service-account JSON. Use Rotate in the UI to replace a stored secret without clearing the rest of the form. | sk-proj-... |
| Enable provider | Yes | Toggle on to expose the provider with this configuration. | toggle |
Repeat for each provider to expose.
Step 4: configure LLM models
The wizard shows a single list of all models Agent Router supports, maintained by Tetrate. By default, a selective set of common models is enabled. Deselect models to control cost, meet data-handling requirements, or scope to the intended use case. Models remain configurable later from the Admin Console. If a required model is missing, contact Tetrate support.
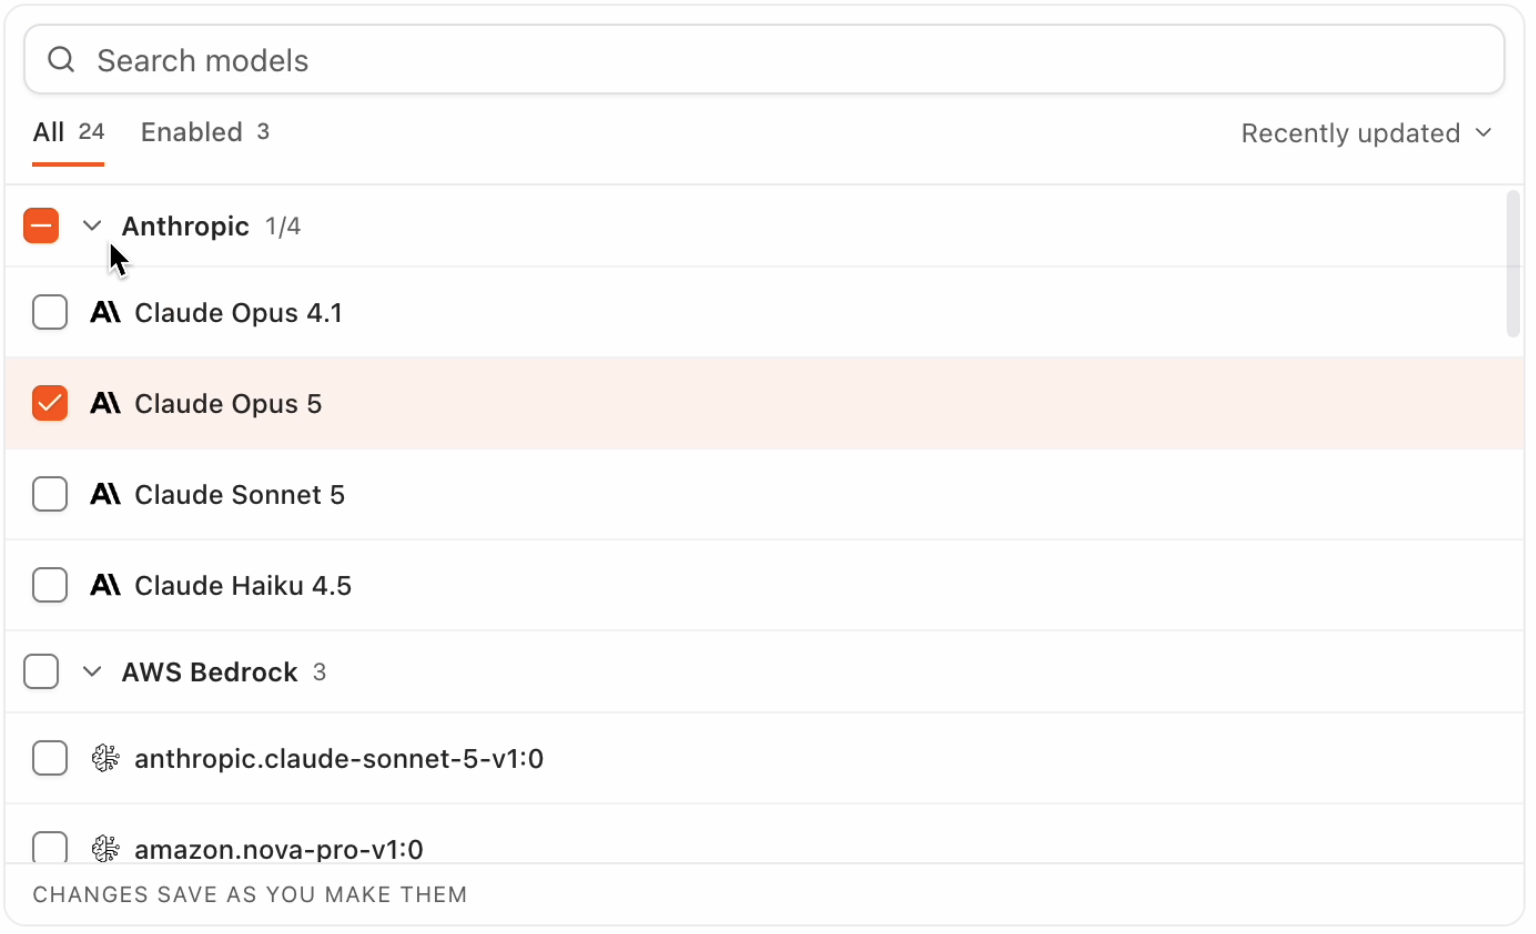
Models can be added during onboarding and at any later time from the Admin Console. Models selected here are added to the default project automatically; models added after onboarding are not added to any project and must be granted manually.
Custom model entries are not configurable in onboarding.
Step 5: configure data plane
This final step generates the credentials the data plane uses to authenticate to the management plane.
Click Create Credential. A data-plane-credentials-default.json file downloads. The credential is valid immediately and can be used to run tare install as soon as it lands.
The download is one-shot. If the browser blocks it or the file is lost, the same credential cannot be downloaded again; regenerate it instead (see below).
Treat data-plane-credentials-default.json as a long-lived secret. Store it in a secret manager; do not commit it to source control.
Regenerate the service account file
If the file is lost before the data plane is installed, regenerate it from the Admin Console:
- Sign in to the Admin Console.
- Go to Directory → Data Planes.
- Select the default data plane.
- In the pop-out panel click Rotate credential and accept the pop-up.
A new data-plane-credentials-default.json file downloads, and the credential it replaces is revoked in the same operation. Only one credential is active per deployment, so older files stop working.
Once the data plane is running, regenerating the credential is a rotation: the running data plane keeps using the file it was installed with, which is now revoked, and stops serving. Follow Data plane credentials instead.
Complete the process
Click Complete setup to finish onboarding.
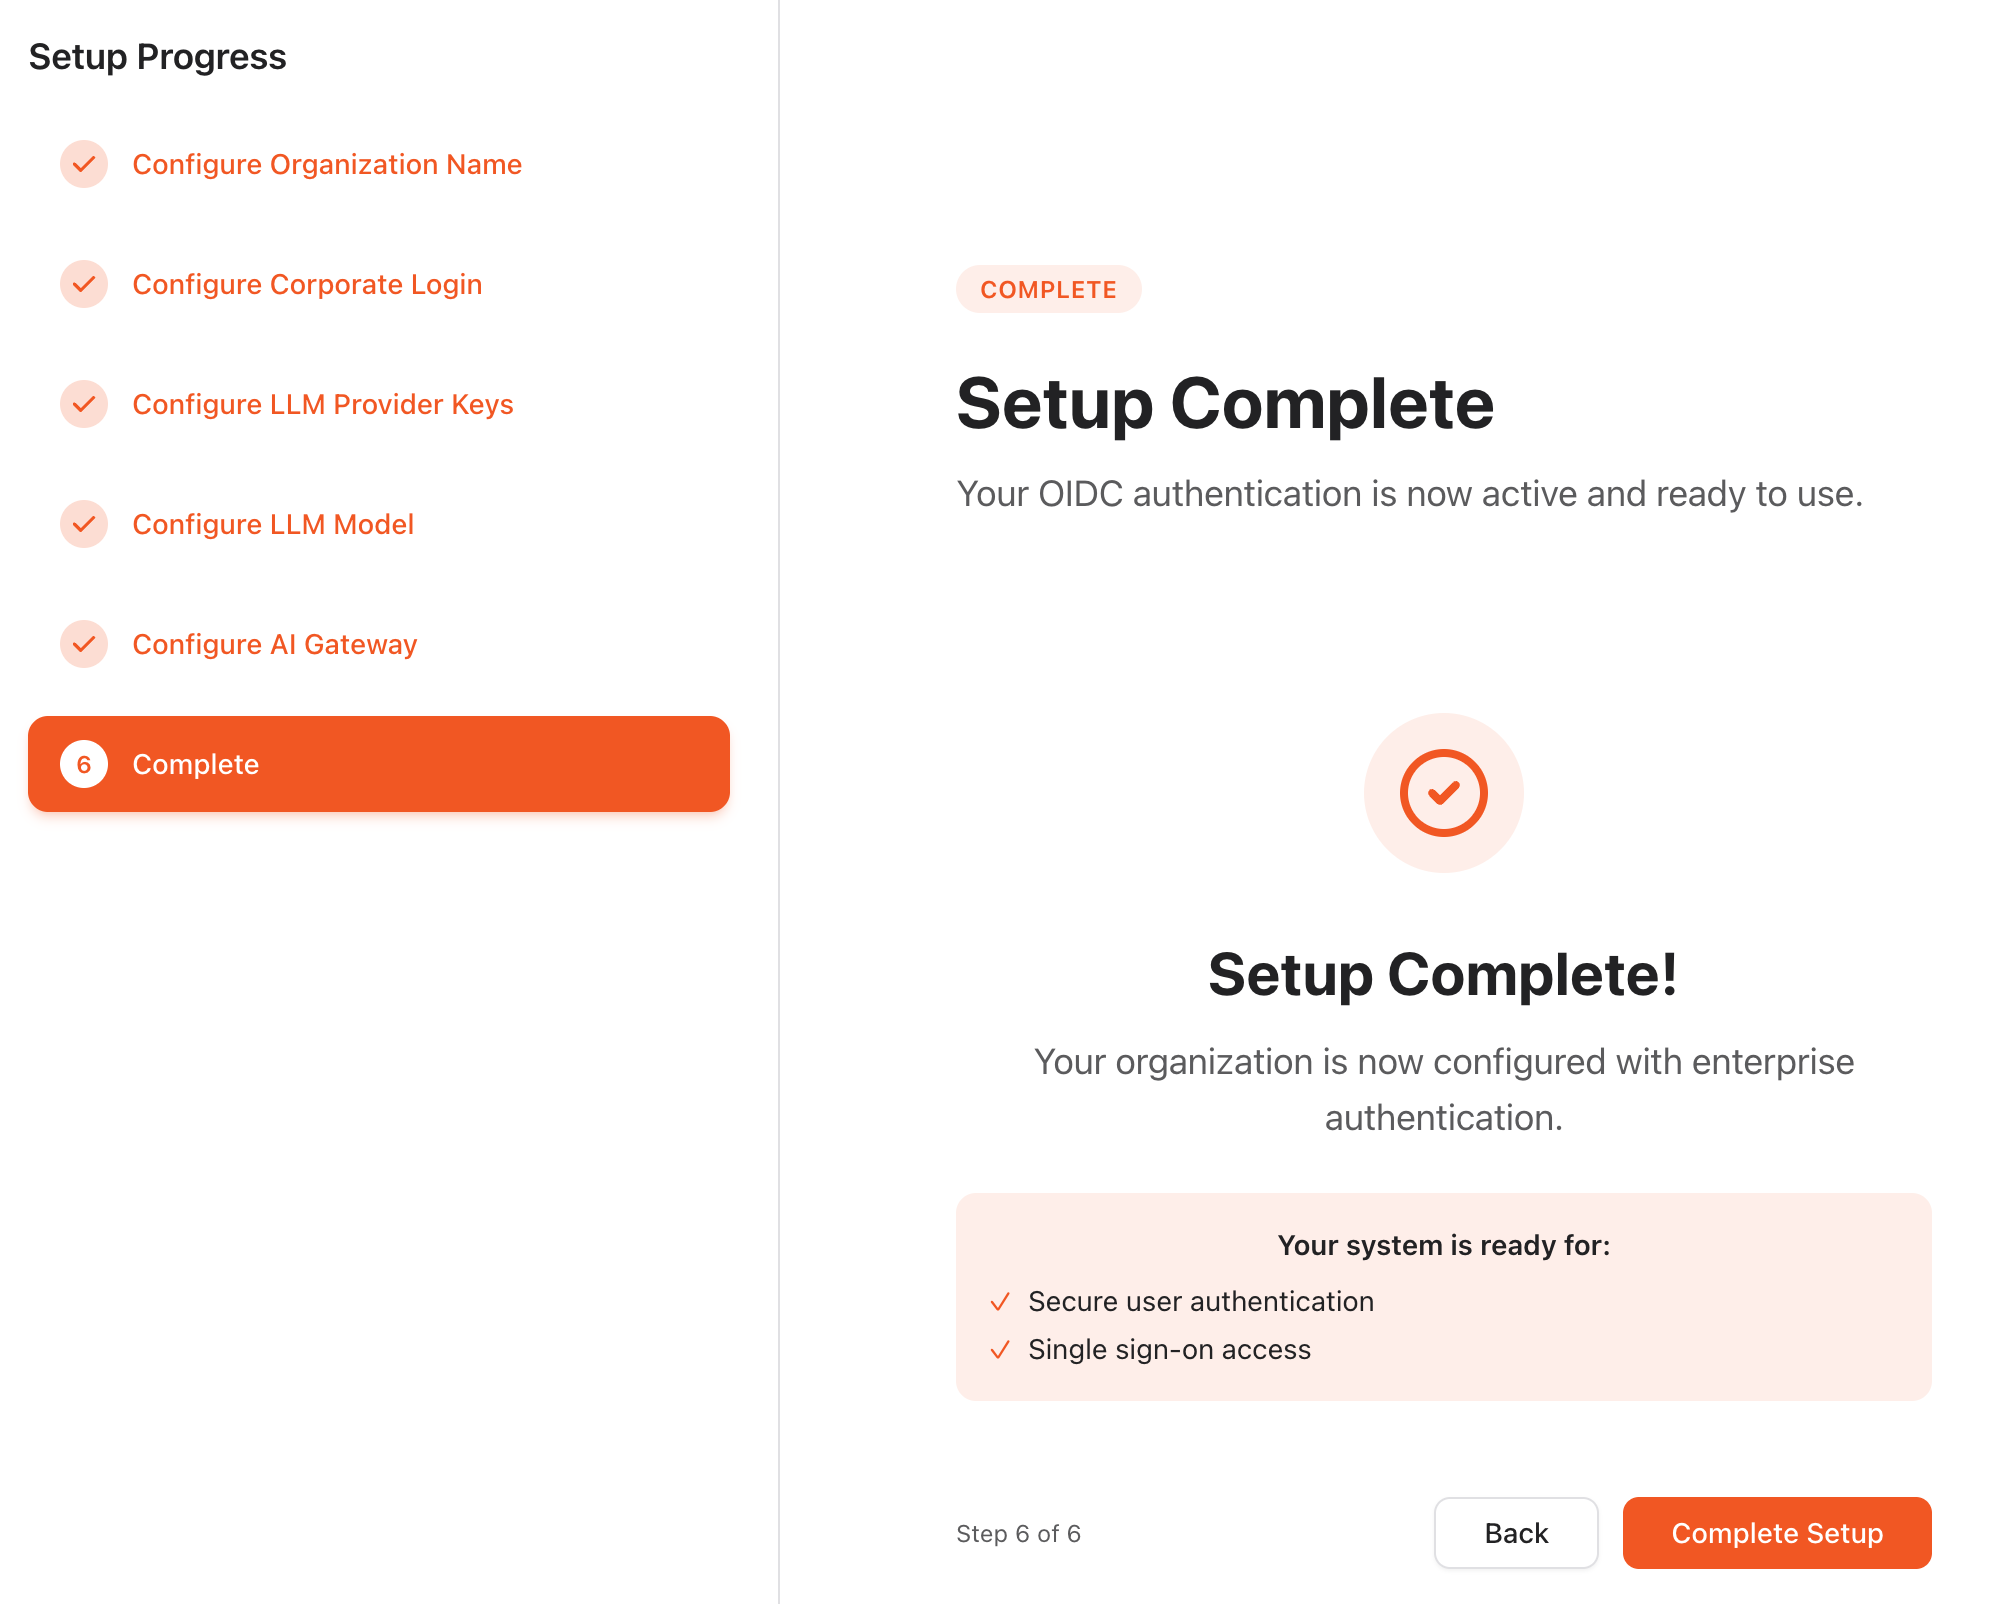
The account that completed the wizard holds the Super Admin role, which carries full access to every resource and setting. Super Admin can be granted to further users from Directory → Access at any time. Grant it to at least one colleague early: a lone holder leaves no route back into administration if that account is lost. The grant, edit, and revoke flow is covered in Manage roles and permissions.
Where to go next